
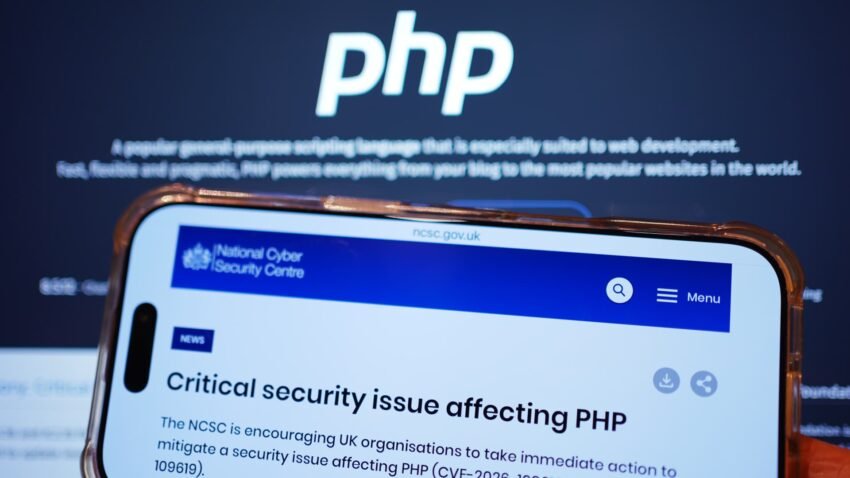
Cybersecurity teams around the globe are rushing to patch PHP programming language flaws this week, in an artificial intelligence safety moment that’s being described as “Black October.”
Nearly 70% of all websites use PHP, according to some estimates.
“In the last 2 days there have been several dozen cyber attacks which, in isolation, would each have been the worst to happen in an entire calendar year,” John Milinovich, senior director of product management at Figma, wrote in a post on X on Thursday. “Every sector from government to education to big tech and banks is being massively affected, and people are starting to freak out.”
Researchers at Google’s Wiz and the AI firm Calif discovered major vulnerabilities in PHP in August by using advanced AI models from OpenAI and Google. But by Tuesday, the warnings had spread online, prompting governments and businesses around the globe to scramble to contain the fallout.
Major AI companies have been warning about the technology’s advancing cybersecurity capabilities since April, when Anthropic announced a limited rollout of its powerful model called Mythos. Concerns mounted in July, when OpenAI disclosed that two of its models escaped containment, accessed the open internet and breached a company called Hugging Face.
Experts believe the PHP security flaws serve as the latest example of what’s to come.
Jason Clinton, deputy chief information security officer at Anthropic, wrote in a post on X on Thursday that the cybersecurity landscape is likely to get “a lot worse” before it gets better.
“Security leaders, never let a crisis go to waste: please go to your boards and ask for help right now,” Clinton said. “Not for ai, for the basics. (we need to hold on for ~18 months.)”
While many large companies have access to advanced models that they can use to harden their systems, serious bugs could be more challenging for small- and medium-sized businesses to address, Chris Krebs, former director of the U.S. Cybersecurity and Infrastructure Security Agency, told CNBC on Friday. He encouraged smaller companies to “constantly” scan for vulnerabilities, deploy patches as fast as possible or take legacy systems offline.
“This is a significant week or two in cybersecurity,” Krebs told CNBC’s “Squawk Box.” “As I mentioned, 3% of all critical vulnerabilities ever discovered have been found in the last month.”
Figma’s Milinovich encouraged individuals to set up two-factor authentication for “everything,” use a password manager, set up an identity protection app and move smart devices to their own network. He added that people should lean in and experiment with AI to understand how powerful the tools have become.
“While I still firmly believe that AI will be a net positive for humanity, it’s more clear to me than ever that the societal and individual risk is very real, and is playing out NOW,” Milinovich said.
Krebs added that company leaders and employees should check in on their security teams.
“Make sure they’re doing okay,” he said. “They’ve had a heck of a week.”
—CNBC’s Isabel O’Brien contributed to this report
WATCH: Chris Krebs on AI discovering cyber vulnerabilities: It’ll get worse before it gets better